

- The project needs at least one completed scan. See Your first scan.
- Triage the findings first. An SBOM records your current decisions, so a project you haven’t triaged produces an SBOM with low review coverage. See Triaging findings.
- You need the Operator or Admin role to make exports, render, or delete snapshots. Anyone who can read the project, Viewers included, can download existing documents. An API key needs
scans:writeto generate andscans:readto download.
What an SBOM Is, in Earnie
Snapshots are immutable. Earnie never edits a snapshot. If the inventory or your decisions
change, you generate a new one. A document you sent to a customer last quarter still says exactly
what it said when you sent it.
Making a New Export
Every export starts in the New export sheet. It opens from:- Export in a project’s Dashboard header → New export…. The sheet opens on the scan behind the Dashboard’s figures.
- Export in the Review header or on a scan’s page → New export…. The sheet opens on the scan you’re looking at.
- Reports in the sidebar → New export. The sheet opens on the project’s latest completed scan.
- Scans without an export on the Reports page → New export beside a scan. The sheet opens on that scan.
-
What do you want to export? Pick one of six choices. Each has a line saying what it’s for.
The sheet offers only the choices your organisation’s scanners cover. If the scan you picked can’t supply a choice, the sheet shows it disabled and says why. A scan that ran no cryptography detection, for example, shows CBOM and Export control disabled with “This scan ran no cryptography detection”, so you don’t find out after you export. Select Customize contents to change what the choice holds. See Adjusting the contents.
- From which scan? The sheet names the scan in words: its git ref or name, a short id, and when it completed. A list lets you choose an earlier completed scan. The sheet shows the scan’s component count and review coverage, so you can see what you’re about to freeze.
-
Which format? The sheet lists only the formats the choice can produce, each with a line saying what it’s for. Choose one or more.
Notice produces the notice file, Export control the export-control evidence report, and Report offers HTML, PDF, Excel, and CSV. A report also asks for a template and its sections, and the sheet shows the logo it will carry, or “No logo set” with a link to Settings → Branding. See Reports.
Adjusting the contents
Customize contents opens the sections and switches for the choice you picked. Adding or removing a section changes what the file is called: a custom mix is named by its parts, for example SBOM + CBOM in the ledger.- Open-source components adds the component inventory.
- Include dev dependencies is on the Open-source components section, so it appears only when the snapshot holds them. It’s off by default. A package the lockfile marks as a development dependency, such as a test runner, a build tool, or a package only they pull in, is left out of the CycloneDX and SPDX documents, and the packages it brought in stay attached to whatever depended on it. A package is dev only when every manifest that holds it reaches it through development dependencies. A lockfile that doesn’t say, a package that is also a runtime dependency elsewhere, and a package your code matched in the tree all stay in. The choice is frozen with the snapshot: a later snapshot of the same scan can differ, and an earlier one never changes. A snapshot generated before Earnie left dev dependencies out still lists them. See Dependencies.
- Include transitive dependencies is also on the Open-source components section. It’s on by default. Turn it off to keep only the direct dependencies, the ones a manifest declares, and every component a scanner matched in your code. A package is left out only when the dependency graph shows that another package brings it in and no manifest declares it. A package the graph can’t place, and a scanner match of a package that is also transitive, stay in. Edges between the direct dependencies that stay are kept. Like the dev dependencies choice, it’s frozen with the snapshot. See Dependencies.
- Known vulnerabilities adds the known vulnerabilities (CVEs) of the components in the snapshot. It’s off by default, and switching it doesn’t change the choice. Each advisory names only the affected versions in the snapshot. When several sources report the same CVE, the document keeps the highest severity and scores, and names every source that reported it.
- Cryptographic assets adds detected algorithms, keys, and certificates as CycloneDX cryptographic assets, which makes the document a CBOM (cryptography bill of materials). It appears only when your organisation has cryptography scanning. To export the CBOM alone, choose CBOM instead of switching other sections off.
- AI models adds the identified models with their licence and lineage. It appears only when your organisation has AI provenance. Models come from model files only. If the project has none, the sheet warns “No model files detected; the AI section will be empty. SDK and dataset usage is listed in Review.”
app-cbom-cyclonedx.json, or app-sbom-aibom-spdx.json for a custom mix.
Some scans finished before Earnie began keeping SBOM evidence. They have nothing to freeze, and Earnie doesn’t rebuild them from today’s catalogue. If you choose one, Earnie tells you to run a new scan and stores nothing. The API refuses with 422 scan_evidence_unavailable.
Making an Export for Several Projects
To make the same export for many projects at once, tick them on All projects, or tick rows on the organisation’s Reports page (see Reports across every project), and select New export. The sheet asks the same questions as above, without the scan question: Earnie freezes each project’s latest completed scan and makes the same files for every project. Each project gets its own outcome. A project whose scan can’t supply what you asked for is skipped with its reason, for example because it ran no cryptography detection, and the others carry on. A project whose latest scan has no SBOM evidence fails with the same error as above, and Earnie makes the other projects’ exports.From the Command Line
earnie export downloads a snapshot from the Earnie CLI. Choose the sections with --include (oss, crypto, ai) and the format with --bom-format (cyclonedx, the default, or spdx, which needs oss). It reuses the scan’s newest snapshot with exactly those sections and that format. It generates a new one when there’s no such snapshot, when the newest one is stale, or when you pass --fresh.
The command also makes notices, export-control reports, reports in the template and sections you choose, and compliance packages, and earnie export list shows the exports that exist. See Notices, reports, and compliance packages.
What a Snapshot Contains
This section explains what Earnie records about a snapshot, what its documents say, and how your decisions shape them.What the Snapshot Records
Earnie stamps each snapshot with:- Reviewed, the review coverage when the snapshot was generated
- Components included, the number of components the snapshot lists
- Generated by, the person who generated it
What the Document Says About Itself
- The project it describes. The CycloneDX root component carries the project’s name and an identifier built from its slug (
earnie-project:<slug>). When the scan came from a commit, that commit is the component’s version. A scan of an uploaded archive has no commit, so the version is left out. An SPDX document is titled “SBOM for” the project name. The names are frozen with the snapshot, so renaming the project later doesn’t change a document you already generated. - The dependency graph. When the scan stored a dependency graph, the document carries it. CycloneDX lists
dependencies, and itscompositionssay whether each part of the graph is complete. SPDX usesDEPENDS_ONrelationships. When the scan stored no graph, and in snapshots generated before Earnie recorded one, the CycloneDX composition isunknownand the SPDX document comment says it carries noDEPENDS_ONrelationships. Don’t read either as “no dependencies”. - What SPDX leaves out. SPDX can’t describe cryptographic assets or AI models. An SPDX document of a snapshot that includes them leaves them out, and its document comment says how many it left out. The CycloneDX document of the same snapshot carries them.
- Concluded and detected licences. A component you confirmed carries the licence you concluded and, next to it, the licence the scan detected. CycloneDX records them as separate licence entries marked
concludedanddeclared. SPDX records them aslicenseConcludedandlicenseDeclared. - Generating tool. Every CycloneDX and SPDX document names
earnieand the build that generated it as its tool, so a document filed with an auditor says which release produced it. If you render a format later from the same snapshot, that document names the build that rendered it, which can be a newer release.
Cryptographic Asset Details
When Cryptographic assets is on, the CycloneDX document has extra detail for each asset:- Export-control metadata. Each cryptographic-asset component has
scanoss:exportControl:*properties. They record the rolled-up signal state, the asset’s purpose, and the control regime and regime version Earnie evaluated the signals against. - Sizes. Key, nonce, salt, and IV assets have their size under
relatedCryptoMaterialProperties.size, when Earnie resolved it. - Key length as parameter set. Some algorithms, such as RSA or AES, use a key length in bits as their parameter set. For these, a resolved key size fills
algorithmProperties.parameterSetIdentifier(for example2048) when the scanner didn’t supply one. Earnie skips post-quantum, hash-based signature, and elliptic-curve algorithms, because their parameter set isn’t a key length. - Curves. Elliptic-curve algorithms have their curve under
algorithmProperties, when Earnie resolved it.
How Decisions Carry into a Snapshot
A new snapshot uses each finding’s current decision, never a withdrawn or superseded one.- Reopening a finding restores its unreviewed evidence for the next snapshot.
- Excluding or replacing one occurrence of a component doesn’t remove another occurrence of the same component that’s still present.
- If the remaining occurrences disagree on known component metadata, such as the version or the concluded licence, generation stops with a
resolution_conflicterror. Reconcile those findings’ decisions in Review, then generate again. Existing snapshots and downloads don’t change.
CRA SBOM Annex
The CRA SBOM annex is a CycloneDX 1.7 export for the EU Cyber Resilience Act (CRA). It always includes the detected cryptographic assets as components. It accompanies the product SBOM, and it isn’t a CRA conformity assessment. You can’t choose the annex in the New export sheet or with the Earnie CLI. It’s generated only through the API, by asking for thecra-sbom-annex format when you generate a snapshot, and only from a scan whose cryptography detection completed. You can’t render it later from an existing snapshot. When a snapshot has one, its row shows a CRA chip that downloads it.
Not the same CRA reference as a policy. The annex isn’t tied to a specific CRA clause. The
CRA — Annex I(2)(e) and CRA — Annex I Part II(1) regulatory template
sets are policies, not
an SBOM export. All three carry a “CRA” label, but they’re unrelated features.
The Reports Page
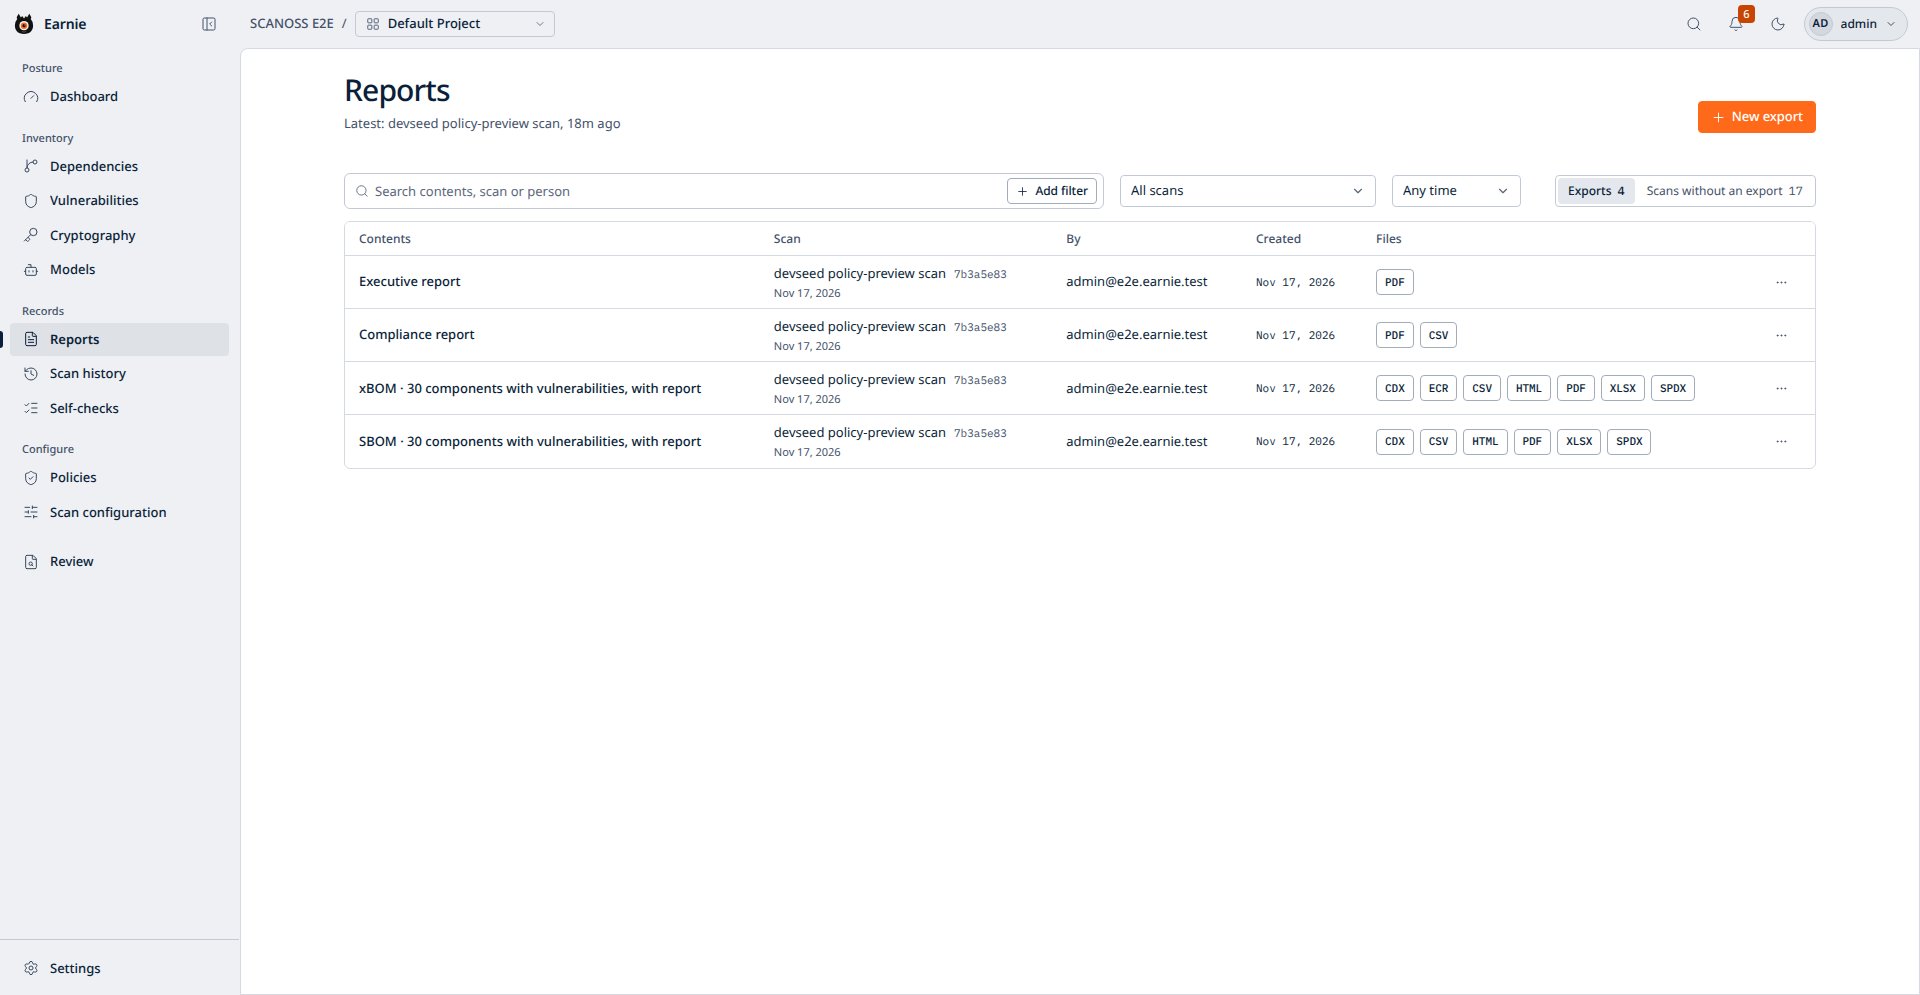
The Reports page lists every export of the project, newest first. Each row shows what the export contains in words, for example “SBOM · 30 components with vulnerabilities”, “CBOM”, or “Executive report”; the scan it came from, with its short ID and date; who made it and when; and a chip for each file it holds. The stamp described in What the Snapshot Records is part of the export. A project with no export shows one sentence and New export. The chips are:
Select a chip to download that file.
Filtering
The filters above the table all live in the page’s address, so you can send a filtered page as a link.The Row Menu
Each row’s menu lets you:- Add a format: render a document the export doesn’t have yet, for example SPDX, Notice file, or Report (PDF). Earnie downloads it at once and the row shows its chip.
- Copy link: copy an address that opens the Reports page on that one export.
- Delete: remove the export and its files, after you type its ID to confirm. The scan isn’t affected.
When an Export Is Out of Date
If triage has changed since an export was made, its row shows a Stale badge. Hover it to see “Triage has changed since this export was made.” The files still reflect the decisions in force when it was made, so select New export and choose that scan before you send it out.Reports Across Every Project
The organisation has a Reports page of its own, in the sidebar at the organisation level, beside Projects. It lists every export of every project, newest first. It is the place to start when someone asks for the latest SBOM of every product. A row reads like a row of a project’s Reports page, with one more column, Project, which opens that project’s own Reports page. You see the exports of the projects and scanners your role or API key can read, and archived projects are left out. The list loads 50 exports at a time. Select Load more to add the next page. The filters above the table live in the page’s address, so you can send a filtered page as a link.
A row’s menu has Copy link, which opens the page on that one export. To add a format or delete an export, use the project’s own Reports page.
Making Exports from the List
With the Operator or Admin role, each row has a checkbox. Tick rows and select New export in the strip to make an export for the projects those rows belong to. A project ticked twice counts once. A project that has never been exported has no row, so use All projects to export it.Following a Bulk Export
An export for several projects is one run. After you select Export, a banner above the table shows how many projects are done and what happened to each:- Made, with Open export, which opens the list on that export. Each made export appears in the table as its project finishes.
- Skipped, with the reason: the project has no completed scan, the package isn’t available to your organisation, its scan ran no cryptography detection, or SPDX needs open-source components. A skipped project makes nothing.
- Failed, with what went wrong. When only a file couldn’t be rendered, the export Earnie had already frozen is kept and listed.
Snapshot Reports
A snapshot report is the snapshot written for a person rather than a tool. It describes one snapshot’s inventory. To choose a template and sections, and to cover the project’s posture including its merge gate, make a report from the New export sheet. See Reports. Add a snapshot report from the export’s row menu, under Add a format. A report you add this way uses the template and sections of a report file the export already has, else the Compliance template with every section you can see:
Adding a format downloads the file at once. After that, the row shows a chip for it that downloads the same file. Through the API, render one with
POST /v1/sbom/snapshots/{snapshotId}:render and a format of report-html, report-pdf, report-xlsx, or report-csv.
Every format has the same sections:
- Summary shows what the snapshot holds, and the review coverage per area.
- Components and licenses lists each component with its licences, and whether a reviewer concluded them or the scan only detected them.
- Vulnerabilities lists known vulnerabilities, worst first.
- Crypto inventory and AI models appear only when the snapshot includes them and you can see that scanner’s results.
- Review state shows how many findings were decided and how many were still open, per area.
- Policy results shows each policy’s action, how many findings it flagged, how many an approval covers, and how many still gate.
Frozen at generation. Earnie captures the review state and policy results
when it generates the snapshot, so a report you render next month shows the
review as it was then. A snapshot generated before Earnie captured this state
still renders a report, and says the state wasn’t captured.
- Safe to open. In the CSV report, a cell a spreadsheet would read as a formula starts with an apostrophe. The Excel workbook stores every value as text. Opening a report never runs anything.
- Non-Latin text in the PDF. The PDF font covers Latin, Greek, and Cyrillic. It can’t show characters outside those scripts, such as Chinese or an emoji, and the PDF’s first page says how many cells are affected. The HTML and Excel reports show those cells in full.
- Logo. The HTML and PDF reports and the Excel cover sheet show your organisation’s logo if an Admin has set one in Branding. The logo is the one set when the snapshot was generated. The CSV report has no logo.
The Export-Control Evidence Report
Some countries control the export of software that uses cryptography. The export-control evidence report collects the evidence you need to classify your own product under those rules. When a snapshot was generated with Cryptographic assets on, from a scan that ran cryptography detection, its row shows an ECR chip that downloads the Export-control evidence report. The report is a self-contained HTML file, frozen with that snapshot. It records:- the detected cryptographic assets
- their export-control signals
- the detection surface it cites, meaning what was scanned
- the identity of the ruleset Earnie used
The report doesn’t claim that all your cryptography is standard. Signature-based detection
can’t prove that no non-standard cryptography is present, so the report marks the statement
“all detected cryptography maps to published standards” as not established from frozen evidence.
To cover a later scan, generate a new snapshot with Cryptographic assets on.
Notice Files (Attribution Documents)
An SBOM and a notice file are different documents, and one can’t replace the other:- An SBOM lists what’s present and names each component’s licence.
- A notice file, also called an attribution document, contains the text you’re obliged to distribute. An OSPO (Open Source Program Office) ships it with a release.
- its licences: the ones a reviewer concluded, or the detected ones where nobody concluded any
- its copyright holders
- its obligations
- the full text of its
LICENSEandNOTICEfiles
Rendering a Notice File
Choose Notice in the New export sheet to freeze a scan and download its notice file in one step. To add one to an export that already exists:- On the Reports page, open the export’s row menu.
- Choose Add a format, then Notice file.
Frozen on first render. The first time you render a snapshot’s notice file, Earnie fixes
its content. Later downloads return exactly the same file, even if the upstream licence text
changes. Hover the NOTICE chip to see when Earnie fetched the licence text, and compare that
date with what you’re about to ship.
Notice Files Elsewhere in Earnie
The same document is available in two other places:- On a project’s Dashboard, the Download menu offers it as Notice file (NOTICE.txt) once the current scan’s snapshot has one. Until then, Needs attention says “No SBOM snapshot exists for the current scan” or “No notice file has been generated for this scan”, with an action to generate it.
- On All projects, the New export action on the “No notice file” row opens the New export sheet with Notice chosen, for every project the row counts. A project with no current snapshot gets one frozen from its latest completed scan, and the notice file is rendered from it, in one step.
What’s Next
- To give a customer or an auditor a posture report rather than an inventory, see Reports.
- When someone asks, months from now, why a component was accepted, look in the audit log.